MCP connections for AI agents, method by method and no further
Connecting an agent to a system you rely on is a question of permission, not plumbing. With MCP, the standard way agents connect to other systems, you decide exactly what an agent may do there, one method at a time.
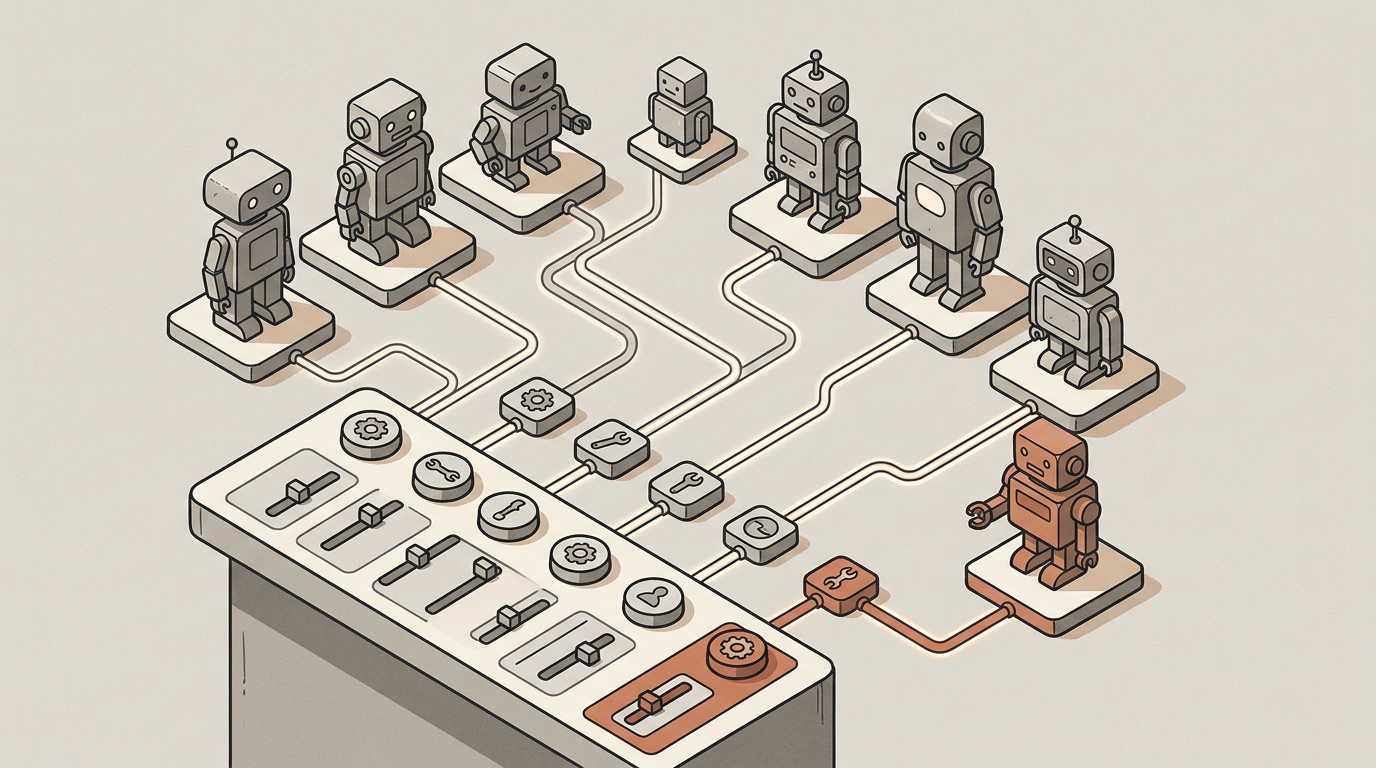
An agent reaches only what you allow
This is not the act layer and not the connection catalogue. A connection built this way lets an agent discover what an external system offers and call those capabilities as tools, but it does so method by method, which is the part that matters. You choose which methods exist for the agent at all, and the ones you don't choose are not refused at run time. They are never there.
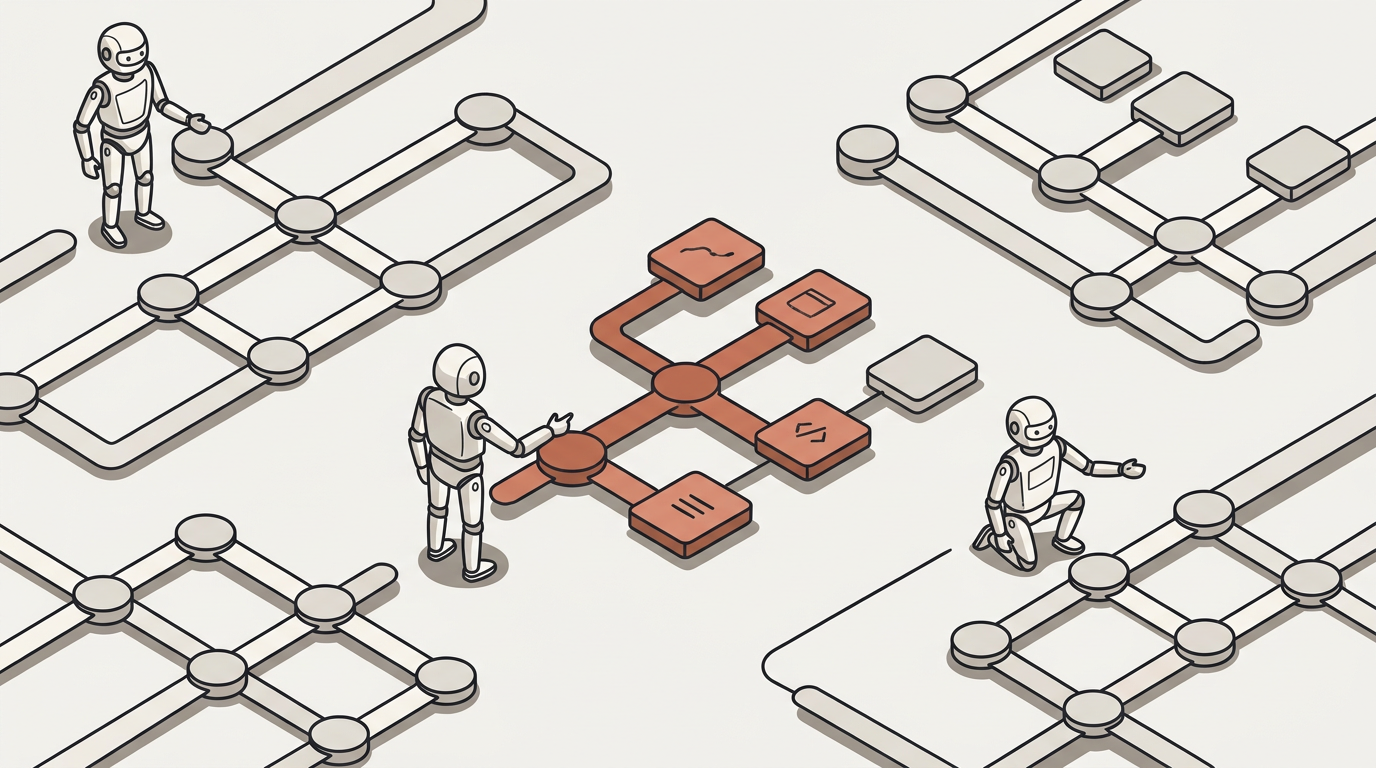
Your own data in that system, and nothing else
You authorise the connection with your own credentials, and where the outside system expects an application of its own, you register that too. The connection reaches your data in that system and nothing else. Where a provider offers sharing, permission or deletion methods, they are left out by design, not left available and trusted not to fire.
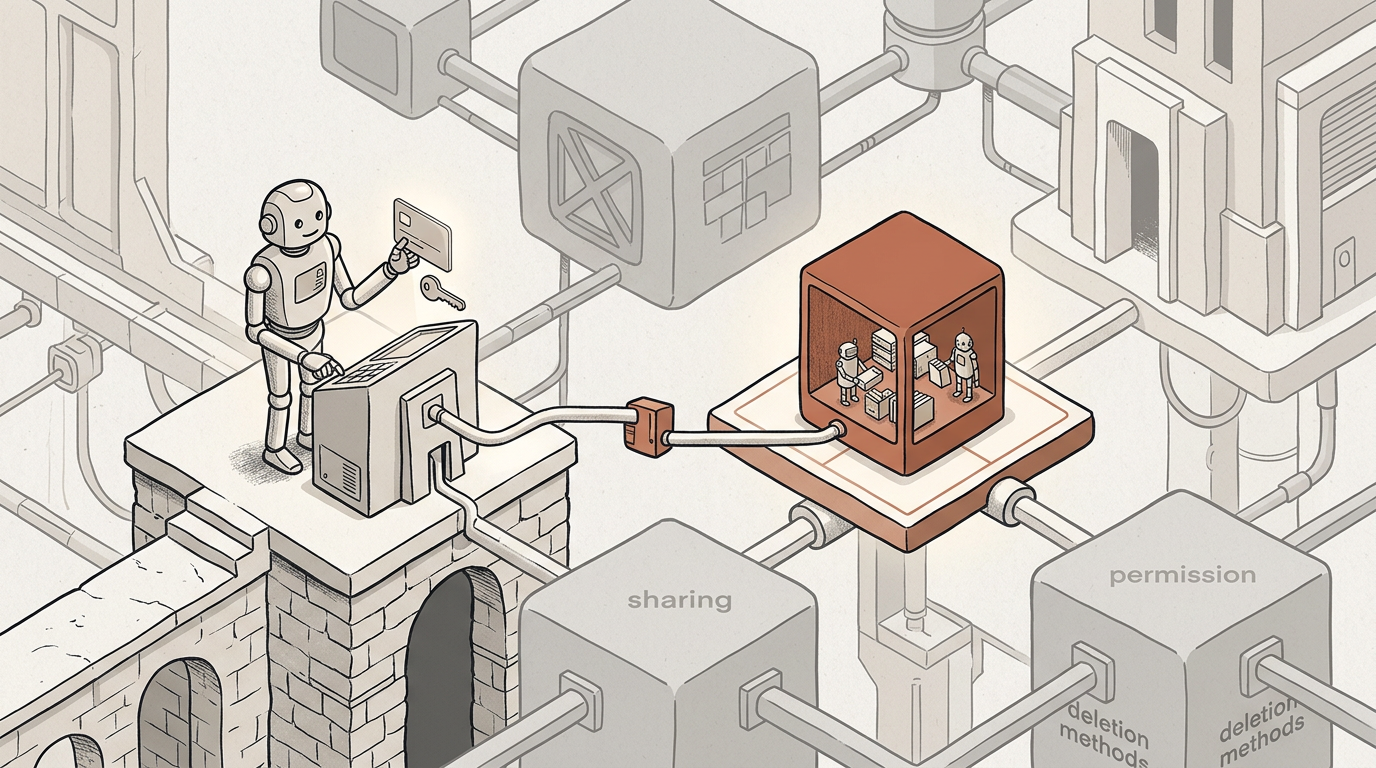
What you can reach this way
The systems you already run, by category
Which specific products are connected today is a question for the demo. It changes, and a page that lists them goes stale.
Your accounting system
Contacts, documents and invoices in the ledger you already keep, read, and written back where you allow it.
Your document storage
Confined to a folder or a shared drive you pin, so a connection that exists for one purpose cannot wander into everything else.
Your own MosenAI records
Contacts, accounts and sessions kept in the platform itself, reachable by an agent under the same per-method control.
Anything that speaks the protocol
A server of your own, or a third party's, over HTTPS, so an in-house system is not a special case that needs us to build something first.
Permission is the product here
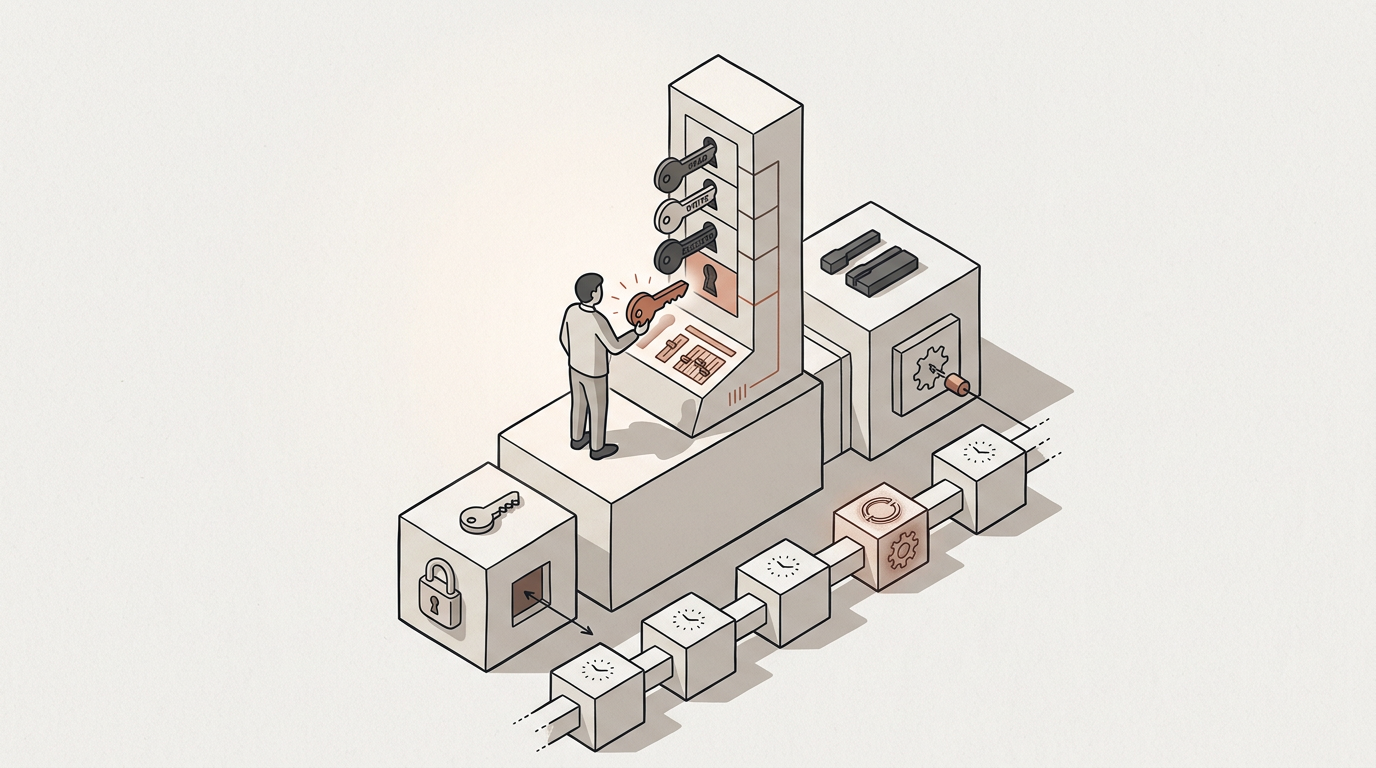
The value is not that an agent can reach your systems, because most things can. It is that you decide, one capability at a time, what it may do there, and that a mutating call inside an unattended run is protected by the same exactly-once ledger as everything else the platform does on your behalf.
- Credentials you generate, verified before they are stored, and encrypted under your own key.
- Sharing, permission and deletion methods are left out by design where a provider offers them.
- A mutating call inside an automation is covered by the same exactly-once protection as every other unattended action.
What you use it for
Start with the system your team retypes into
Document & data processing
The paperwork that arrives as an attachment and leaves as a retyped line.
Read moreBack-office automation
Renewals, closings and filings that run on a calendar, not on somebody’s memory.
Read moreAsk whether it reaches what you run
It is a better question for a conversation than for a page. The honest answer depends on your stack, and it changes.